You sign up, you enter your phone number, and the app needs to know it’s really yours. Traditionally, SMS OTP has done that job, with a few caveats: codes can be phished, intercepted through SIM swaps, or simply never arrive, and every one of them costs money.
Network-based authentication, where you verify the user through the mobile network instead, is the more secure, seamless option.
That’s something Firebase Phone Number Verification (PNV) does with SIM-based phone number verification. But what happens when that method isn’t available?
Network verification beats SMS OTP, but no single network method works for every user. And that’s where this conversation grows bigger than PNV: not one additional authentication method, but an adaptable authentication that orchestrates them.
What Firebase Phone Number Verification Does, and Doesn’t
Firebase PNV uses GSMA TS.43-based SIM credentials to provide SIM-based phone number verification without requiring the developer to build carrier integrations themselves.
To verify a phone number, Firebase checks whether the device and mobile operator are supported, gets the user’s consent, and then works with the operator to verify that the phone number is assigned to the SIM card.
No SMS is sent and there is no OTP to enter, already a significant improvement.
The flow still requires explicit user consent, though. That comes with SIM-based verification itself, not with Firebase specifically, but it means this path never removes all user interaction.
Then there’s reach. Firebase PNV currently supports participating operators across 12 markets, with Google continuing to expand coverage. If the user isn’t using an Android device or a supported operator, Firebase recommends going back to the OTP route.
That isn’t a flaw in PNV. It’s what happens with any single authentication channel. PNV cannot be the only authentication path for every user, and the developer still needs to account for what happens outside the Firebase PNV flow.
IPification Goes Beyond SIM-Based Verification
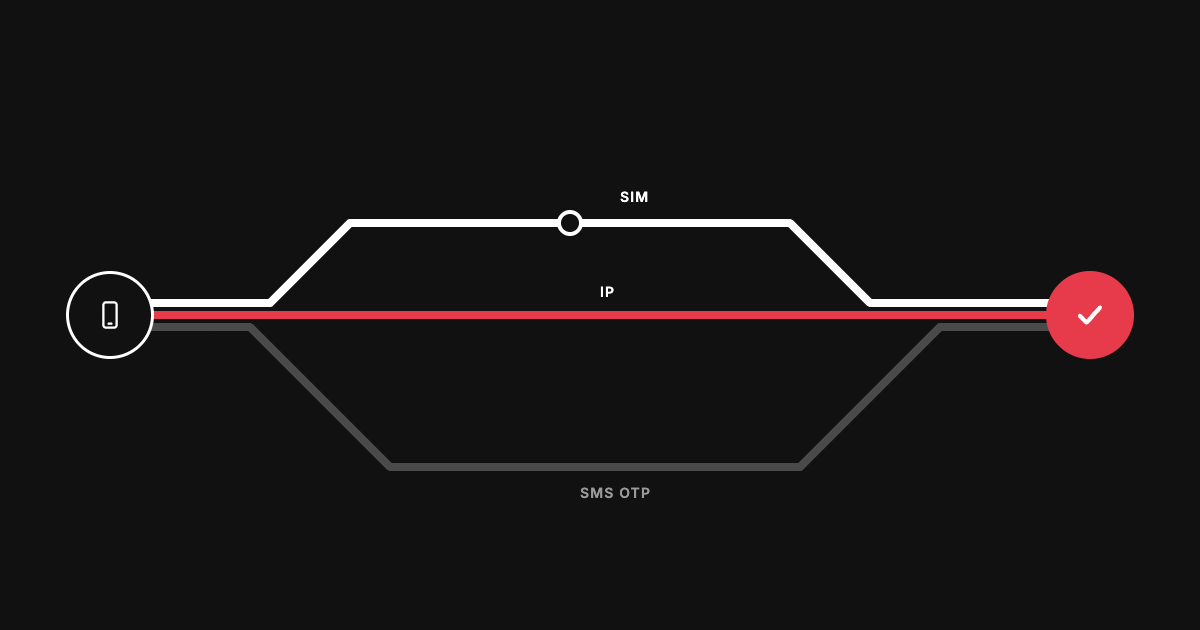
IPification supports both SIM-based and IP-based verification.
When IP-based authentication is available, the active mobile data connection can verify the user silently, in the background. When it isn’t, SIM-based authentication provides another route. That’s the key difference for the user: IP-based verification can happen without the user doing anything, while SIM-based verification asks them to confirm the authentication.
IPification also actively works with mobile operators to enable and expose network authentication capabilities, then aggregates those capabilities for enterprises. Today, IPification is live in 40 markets, with 20 more deploying, reaching 4.9 billion people.
On the application side, our Adaptive Authentication SDK is designed to handle variations in network conditions, carrier availability and authentication channels. In other words, the developer does not have to treat every authentication method as a separate integration.
Developers define the order of preference, and the SDK picks the best available path.
For example, if a user is on Wi-Fi and IP-based verification can’t be completed, the flow can either use SIM-based verification or even route the authentication request over the cellular network. If network authentication still can’t be completed, the flow can move to another fallback, such as SMS OTP. But when network authentication is possible, the verification typically completes in under two seconds.
So yes, every authentication journey can still end at SMS OTP. The difference is how many network routes you try before you get there, who decides the logic, and how easy it is to manage.
The true benefit is being less dependent on any single authentication method.
For users, that can mean fewer unnecessary steps and fewer SMS OTP journeys. And that means more conversions: friction during signup and login can cause users to abandon the journey altogether. Over 60% of consumers say they have abandoned a transaction because of authentication frustration.
For enterprises, it means more flexibility across different operators, devices and network conditions. And for developers, it means less carrier-specific logic to build and maintain.
Whereas Firebase PNV gives developers a convenient way to use one network authentication capability, IPification is built to sit across the authentication journey.
What Enterprises Should Look for in Phone Verification
Replacing SMS OTP is a good start, but we have to take many factors into consideration.
Enterprises should look at:
- Available authentication paths: Is the solution tied to one method, or can different network methods work together?
- Fallback: What happens when the preferred method can’t be used?
- UX: How often can verification happen silently, and when does the user need to take action?
- Platform and operator reach: Which users can access each method today?
- Integration complexity: Who handles differences between carriers, network conditions and authentication channels?
- Adaptability: Can new operator capabilities and authentication methods be added without rebuilding the customer journey?
The more authentication paths exist, the better, but they mean nothing if they don’t behave like one coherent system. That’s where IPification fits in.
Learn more about our Adaptive Authentication SDK, or talk to our team about your setup.